Penetration Testing in Charlotte, NC
Charlotte is the second-largest banking centre in the United States by assets held by institutions headquartered in the city: Bank of America and Truist run their headquarters from Uptown, Wells Fargo operates one of its largest employment hubs here, and around them sit the Charlotte Branch of the Federal Reserve Bank of Richmond, insurers and retirement providers such as Brighthouse Financial and TIAA, and a growing fintech and payments community. The same metro is home to Duke Energy, the industrial headquarters of Honeywell and Nucor, Lowe's in nearby Mooresville, the health systems of Atrium Health and Novant Health, and the American Airlines hub at Charlotte Douglas International Airport. HackersHub runs offensive security engagements scoped to the threat model these organisations actually face: fraud and account takeover against digital banking, ransomware and data theft through third-party service providers, identity attacks against large operations workforces, and threats to the grid, together with the GLBA, FFIEC, NERC CIP, HIPAA, PCI DSS and SOC 2 evidence that examiners, auditors and customers expect. HackersHub has also opened 20 complimentary penetration tests to qualifying US companies ahead of its Q1 2027 US expansion; eligibility, agreed scope and availability apply.
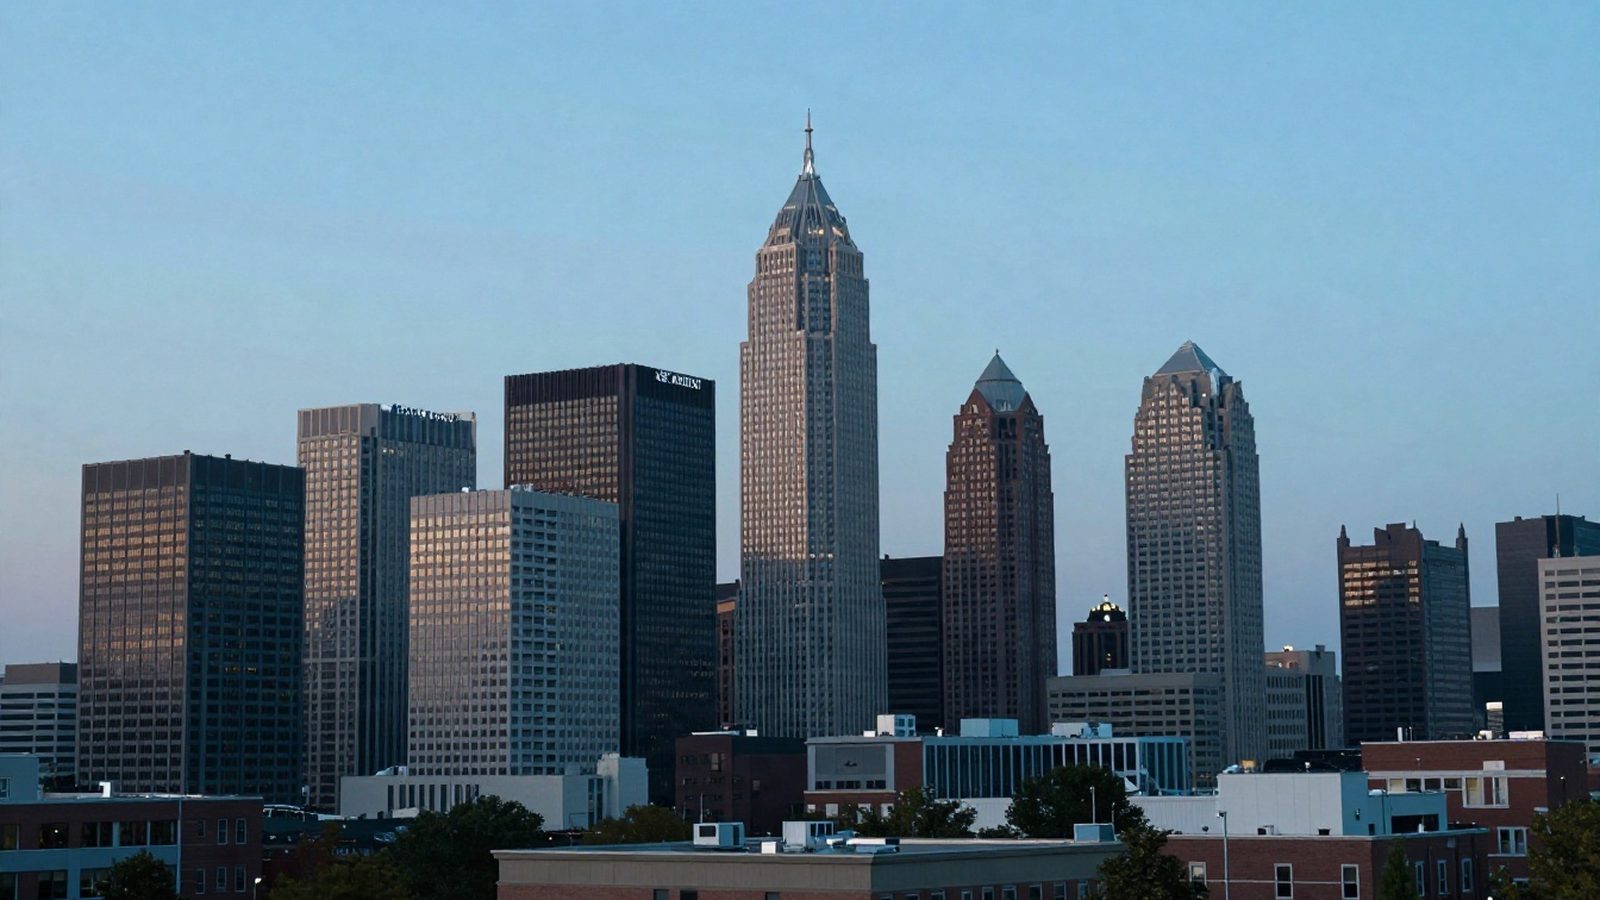
The Charlotte threat landscape
Charlotte's biggest exposure is not the bank's own perimeter but the hundreds of firms that touch its data. In late 2023 a ransomware group compromised a third-party service provider that administered products for one of the city's largest banks, and the bank later notified tens of thousands of customers that names, account details and Social Security numbers held by the provider may have been exposed. Nothing in the bank's own network had to fail for that to happen. Supervisors have drawn the same conclusion: the federal banking agencies' interagency guidance on third-party relationships, finalised in 2023, expects banks to manage security risk across the full lifecycle of a vendor relationship, and the computer-security incident notification rule requires banks to notify their primary regulator within 36 hours of a significant incident and requires bank service providers to notify their bank customers. For Charlotte's fintechs, processors and technology suppliers, that means the penetration test summary is now part of every bank due-diligence questionnaire. The second exposure is scale. Bank operations, technology and contact centres employ tens of thousands of people in the metro, and their identity platforms, privileged-access tooling and help desks are the paths attackers use first. The third is critical infrastructure. In December 2022 deliberate gunfire attacks on two electrical substations in Moore County, in central North Carolina, left tens of thousands of customers without power for days, a reminder that utility security covers physical sites, field networks and the operational technology behind them, not only the corporate IT estate. Health systems headquartered in the metro add a fourth exposure: ransomware aimed at clinical operations, where downtime forces fast decisions. North Carolina regulates the result through the Identity Theft Protection Act, which requires notification of affected residents and of the Consumer Protection Division of the Attorney General's office without unreasonable delay after a breach. Engagements in Charlotte routinely uncover vendor connections with broader access than the contract allows, service accounts shared between bank applications and their supporting platforms, help-desk processes that can be talked into credential resets, and IT-to-OT paths in utility and industrial environments that were assumed to be closed.
Need a penetration test in Charlotte?
Written scope, named OSCP-certified testers, report within a week of the last testing day.
Industries we routinely engage in Charlotte
The sectors that dominate Charlotte's economy, and what each one needs a penetration test to prove.
Banking & financial institutions
Bank headquarters, operations and technology centres, regional and community banks and credit unions. External and internal penetration tests, digital and mobile banking application testing, identity and privileged-access assessments, help-desk social engineering testing and red team operations. Evidence mapped to the GLBA Safeguards Rule, the Interagency Guidelines Establishing Information Security Standards, the FFIEC IT Examination Handbook and NYDFS 23 NYCRR 500 for New York-licensed entities. Our banking guide at /insights/penetration-testing-for-banks-and-credit-unions/ sets out examiner expectations.
Fintech, payments & bank service providers
Fintechs, payment processors, core and digital-banking vendors and the service providers that sit inside bank supply chains. Manual web-application and API penetration testing of onboarding, payment and open-banking flows, cloud-configuration review, and the attestation letters and summary reports banks request in vendor due diligence. Evidence mapped to SOC 2 Trust Services Criteria and PCI DSS v4.0.1 Requirement 11.4. Our fintech guide at /insights/fintech-penetration-testing/ covers the attack surface.
Insurance, retirement & asset management
Life and annuity insurers, retirement and pension providers and asset managers with Charlotte headquarters or large operations. Policyholder and participant portal testing, adviser and broker API assessments, contact-centre social engineering testing and identity reviews. Evidence mapped to SEC Regulation S-P, the GLBA Safeguards Rule, state insurance data-security expectations and SOC 2.
Energy & utilities
Electric and gas utilities, generation operators, grid-technology suppliers and energy services firms. OT and ICS-aware penetration testing with passive-first methodology, IT/OT boundary and remote-access testing, substation and field-network architecture review, and physical security assessments under a written letter of authorisation. Evidence aligned to NERC CIP, NIST SP 800-82 Rev. 3 and IEC 62443.
Healthcare & health systems
Atrium Health, Novant Health and the physician groups, labs and health-tech vendors around them operate across several states, which multiplies identity stores and network seams. We test how far an attacker gets from a compromised clinician account, whether biomedical and imaging segments really are separated from the business network, and how exposed patient portals and scheduling APIs are. Results support the HIPAA evaluation standard and the state's breach-notification duty; /insights/hipaa-penetration-testing/ explains scope and frequency.
Industrial, retail & aviation headquarters
Industrial-technology, steel and manufacturing headquarters, home-improvement and retail groups, motorsport and logistics companies, and airline and airport operators. External attack-surface and web-application testing, e-commerce and point-of-sale testing under PCI DSS, OT segmentation review for plants and distribution centres, and CMMC 2.0 readiness testing where defence contracts apply.
Compliance frameworks we report against
In Charlotte a penetration test report rarely stays inside the security team. Banks hand it to examiners, service providers hand a summary to the banks that rely on them, and utilities file evidence under NERC CIP. We therefore deliver a testing statement and attestation letter for outside readers, an executive summary for the board, a reproducible technical report for engineers and a remediation tracker that shows closure. For statewide context, including Raleigh and the Research Triangle, see our North Carolina page at /north-carolina/.
- North Carolina Identity Theft Protection Act (N.C. Gen. Stat. 75-60 and following): notification of affected residents and of the Consumer Protection Division of the Attorney General without unreasonable delay, and secure disposal of personal information
- GLBA Safeguards Rule (16 CFR Part 314) and the Interagency Guidelines Establishing Information Security Standards for banks
- FFIEC IT Examination Handbook and the 2023 Interagency Guidance on Third-Party Relationships: Risk Management
- Computer-Security Incident Notification Rule: notification of the primary federal regulator within 36 hours of a notification incident, and service-provider notification to bank customers
- SEC Regulation S-P as amended in 2024, and Form 8-K Item 1.05 disclosure of material cybersecurity incidents for listed banks, insurers and industrial companies
- New York DFS cybersecurity regulation, 23 NYCRR 500.5, for Charlotte institutions that hold a New York charter or licence
- NERC CIP reliability standards for bulk electric system cyber assets
- HIPAA Security Rule evaluation duty (45 CFR 164.308(a)(8)) for health systems and their business associates
- PCI DSS v4.0.1 penetration and segmentation testing (Requirement 11.4) for retail, e-commerce and card-issuing environments
- SOC 2 Trust Services Criteria, the reports banks request from fintechs and service providers
- Federal Reserve, OCC and FDIC supervisory expectations for independent testing of information security programmes
- NIST SP 800-115 for test planning, execution and reporting
Services delivered for Charlotte engagements
The same HackersHub services, scoped for bank examiners, vendor-risk teams and grid operators.
See also:Penetration Testing in North CarolinaPenetration Testing in AtlantaPenetration Testing in United States
Why Charlotte organisations choose HackersHub
Charlotte buyers usually ask two things first: who actually does the testing, and where are they based. The answer is a practitioner team from Amsterdam, founded in the Netherlands in 2015, with more than 2,500 completed security engagements and no office in the United States. Application, API, mobile, cloud and external testing is performed remotely from the Netherlands. Internal network, Active Directory, wireless, OT and physical work is performed in Uptown, SouthPark, Ballantyne or wherever the systems sit, by testers who travel in, with vetted US delivery partners alongside when a bank or utility prefers it. HackersHub already serves US clients that way and is preparing a full-scale US market entry for Q1 2027. Michael van Mameren (OSCP) is engagement lead; every tester is OSCP-certified, and the team includes OSWE and CREST holders. Reports are drafted against GLBA, FFIEC, NERC CIP, HIPAA, PCI DSS and SOC 2, an attestation letter for vendor due diligence is available on request, medium-and-above findings are retested within 90 days, and a senior tester books your scoping call on Eastern time within one business day.
Frequently asked questions: Charlotte
Ready to Secure Your Systems?
Request a quote for your penetration testing needs.