Penetration Testing in Seattle, WA
The Puget Sound region runs a large share of the world's cloud and online commerce: Amazon and AWS in South Lake Union, Microsoft and Azure across the lake in Redmond, the SaaS, travel and real-estate platforms of Bellevue and downtown Seattle, Starbucks, Nordstrom and Costco in retail, T-Mobile in telecoms, Boeing's commercial-airplane plants in Everett and Renton with hundreds of aerospace suppliers around them, Fred Hutchinson Cancer Center and UW Medicine in healthcare and research, and the Port of Seattle with Sea-Tac Airport and the container terminals. HackersHub runs manual offensive security engagements scoped to what these organisations actually face: cloud control-plane and identity attacks, e-commerce and payment abuse, ransomware against public infrastructure, supply-chain intrusion into aerospace programmes, and the HIPAA, PCI DSS, SOC 2, CMMC and Washington privacy evidence that customers and regulators expect.
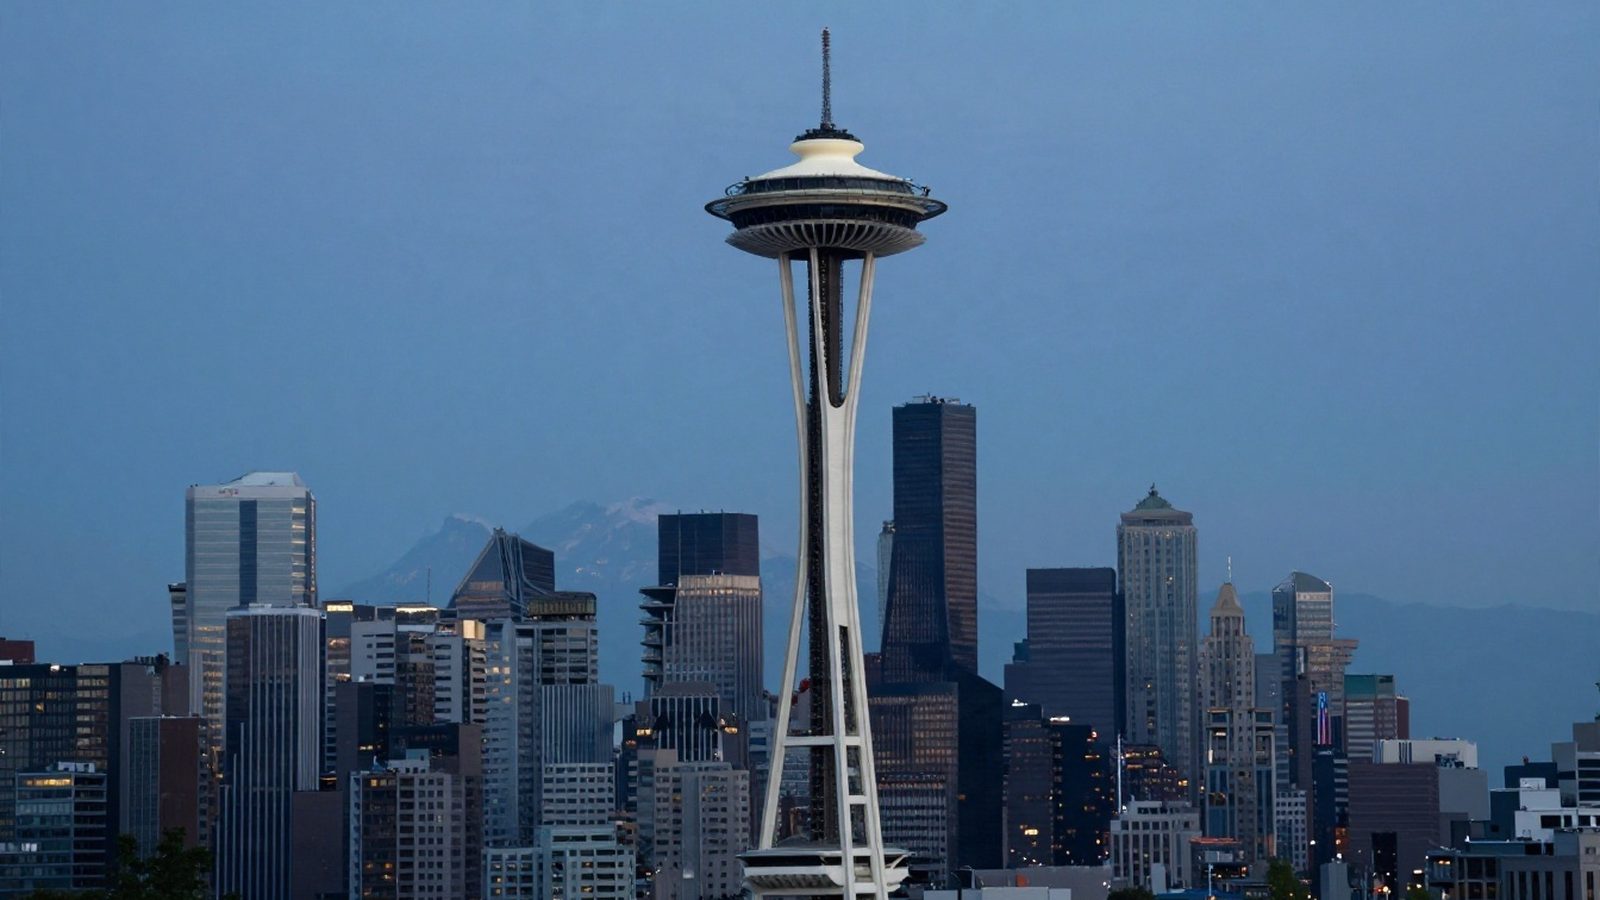
The Seattle and Puget Sound threat landscape
Seattle organisations live inside the cloud platforms built here, and so do their attackers. The decisive attack surface is rarely a server: it is the cloud control plane, the identity provider, the CI/CD pipeline and the metadata services that issue temporary credentials to workloads. A web-application flaw such as server-side request forgery that reaches an instance metadata endpoint, an IAM role that can assume another, or a storage bucket readable by any authenticated principal can turn a minor bug into full data exposure, and those chains are what engagements here repeatedly find. Retail and e-commerce add volume: credential stuffing against customer accounts, gift-card and loyalty fraud, checkout and promotion logic abuse, and the web-skimming scripts that PCI DSS v4.0.1 now addresses explicitly through its payment-page script requirements. Public infrastructure carries a different risk. On 24 August 2024 the Port of Seattle, which operates Sea-Tac Airport, was hit by a ransomware attack later attributed to the Rhysida group; the Port took systems offline, airport baggage, check-in, Wi-Fi and website services were disrupted for days, the Port declined to pay, and in April 2025 it began notifying roughly 90,000 people, mostly current and former employees and contractors, whose personal information had been taken. Aerospace suppliers face state-aligned collection against design and manufacturing data and the Department of Defense's CMMC 2.0 requirements wherever they handle controlled unclassified information. Health systems and research institutes hold clinical and genomic data. Washington adds two legal pressures: the state breach law requires notice to affected residents within 30 days and to the Attorney General when more than 500 residents are affected, and the My Health My Data Act, in force since 31 March 2024, regulates consumer health data far beyond HIPAA and gives consumers a private right of action. Engagements in Seattle routinely uncover over-permissive IAM trust relationships, long-lived access keys in build systems, metadata services reachable through application flaws, flat networks between corporate and operational systems at logistics sites, and supplier VPN accounts with standing access to engineering environments.
Need a penetration test in Seattle?
Written scope, named OSCP-certified testers, report within a week of the last testing day.
Industries we routinely engage in Seattle
Six sectors account for most Puget Sound scopes, each with its own attack paths and its own auditor.
Cloud, SaaS & developer platforms
Cloud-native software companies in South Lake Union, Fremont, Bellevue and Redmond. Cloud penetration testing of AWS and Azure control planes, IAM privilege-escalation analysis, Kubernetes and container testing, CI/CD and supply-chain review, and manual web-application and API testing. Reports mapped to SOC 2 Trust Services Criteria and, for public-sector SaaS, FedRAMP Rev. 5 CA-8. Audit expectations are explained at /insights/soc-2-penetration-testing/.
Retail & e-commerce
Retailers, marketplaces and consumer brands with online and in-store channels. Testing of checkout, promotion and loyalty logic, account-takeover resilience, payment-page script controls, and segmentation of point-of-sale and store networks. Evidence mapped to PCI DSS v4.0.1 Requirement 11.4 and the payment-page requirements in 6.4.3 and 11.6.1. Scoping rules are set out at /insights/pci-dss-penetration-testing/.
Aerospace & advanced manufacturing
Tier 1 to Tier 3 aerospace suppliers around Everett, Renton, Kent and Auburn, and the composites and precision-machining shops that feed them. Internal network and Active Directory testing, engineering and PLM environment segmentation, supplier remote-access review, and OT and shop-floor assessments run passive-first. Evidence aligned to CMMC 2.0 Level 2 and NIST SP 800-171 Rev. 3, with export-control-aware handling under ITAR and EAR.
Healthcare, life sciences & research
Academic medical centres, cancer-research institutes, regional health systems and the biotech and global-health organisations of South Lake Union. Security Rule evaluation evidence under 45 CFR 164.308(a)(8), clinical and research network segmentation, and testing of consumer health apps against the My Health My Data Act. Testing cadence is discussed at /insights/hipaa-penetration-testing/.
Ports, airports & logistics
Port and airport operators, freight forwarders, cold-chain and warehousing companies. External attack-surface and ransomware-readiness testing, Active Directory and backup-infrastructure assessment, segmentation between corporate, operational and tenant networks, and red team operations that measure detection and response. Reporting that supports TSA cybersecurity requirements for aviation and US Coast Guard maritime cybersecurity expectations for regulated facilities.
Telecoms, travel & consumer platforms
Wireless carriers, online travel and real-estate platforms and consumer apps headquartered in Bellevue and Seattle. Mobile-application testing against OWASP MASVS v2, API and account-recovery testing, SIM-swap and help-desk social-engineering scenarios, and identity and privileged-access reviews. Evidence mapped to FCC customer-data rules where they apply, SOC 2 and the SEC cybersecurity disclosure rules for listed companies.
Compliance frameworks we report against
A Seattle report usually serves several readers at once: the cloud security team fixing IAM policies, the PCI assessor or SOC 2 auditor checking scope, the prime contractor reviewing a supplier's CMMC posture, and counsel tracking Washington breach and health-data exposure. Findings are written once and cross-referenced to each of the frameworks below, so no reader needs a separate document.
- Washington data breach notification law (RCW 19.255.010): notice to affected residents within 30 days and to the Attorney General when more than 500 Washington residents are affected
- Washington My Health My Data Act (RCW 19.373), in force since 31 March 2024, covering consumer health data outside HIPAA with a private right of action
- HIPAA evaluation duty in 45 CFR 164.308(a)(8) for hospitals, research institutes and health plans
- PCI DSS v4.0.1 Requirement 11.4 penetration testing and the payment-page script requirements in 6.4.3 and 11.6.1
- CMMC 2.0 Level 2 and NIST SP 800-171 Rev. 3 for defence and aerospace supply chains, with DFARS 252.204-7012
- FedRAMP Rev. 5 CA-8 penetration testing for cloud services sold to federal agencies
- TSA cybersecurity requirements for airport and aviation operators and US Coast Guard maritime cybersecurity rules for regulated facilities
- SEC cyber-incident and governance disclosure (8-K Item 1.05, S-K Item 106) for listed retailers, carriers and platforms
- SOC 2 monitoring and incident criteria (CC7.1, CC7.4) for SaaS vendors
- OWASP MASVS v2 and the MASTG test guide for consumer and carrier apps
- NIST SP 800-115 guidance on technical testing and assessment
Services delivered for Seattle engagements
Cloud and application testing dominate Puget Sound scopes; plant, port and store networks bring in internal, wireless and OT work.
See also:Penetration Testing in Washington StatePenetration Testing in San FranciscoPenetration Testing in United States
Why Seattle organisations choose HackersHub
Seattle splits cleanly into work that can be done from anywhere and work that cannot. Cloud control planes, e-commerce platforms, mobile apps and APIs are tested remotely from Amsterdam by HackersHub, a Dutch practitioner firm founded in 2015 with more than 2,500 engagements behind it. Supplier plants in Everett and Kent, distribution centres, port and airport networks and store estates need people on site, so testers travel to Puget Sound for those windows and vetted US delivery partners extend capacity under our methodology when a programme covers many sites. We have no office in Seattle, Washington or anywhere in the United States, and we say so in every proposal; US market entry at full scale is planned for the first quarter of 2027. The engagement lead is Michael van Mameren (OSCP), every tester carries at least OSCP, OSWE and CREST certifications are held within the team, methodology follows PTES, the OWASP WSTG and NIST SP 800-115, and each engagement includes a retest of medium-or-higher findings within 90 days. The work is rated 4.9/5 across 127 reviews.
Frequently asked questions: Seattle
Ready to Secure Your Systems?
Request a quote for your penetration testing needs.