Penetration Testing in Georgia, USA
HackersHub runs offensive security engagements for organisations across the state of Georgia: the payments and fintech corridor around Atlanta and Alpharetta that the industry calls Transaction Alley, home to Global Payments, NCR Voyix, Elavon and large Fiserv operations; the corporate headquarters of Delta Air Lines, The Home Depot, UPS, Coca-Cola and Equifax; the Port of Savannah and the logistics networks behind it; Emory Healthcare and the state's large hospital systems; and the defence and cyber ecosystem around Fort Eisenhower in Augusta. Testers certified to OSCP, OSWE and CREST level work through each scope by hand, from Amsterdam for anything network-reachable and in person at Georgia sites when cards, cargo or controlled data demand it.
The Georgia threat landscape
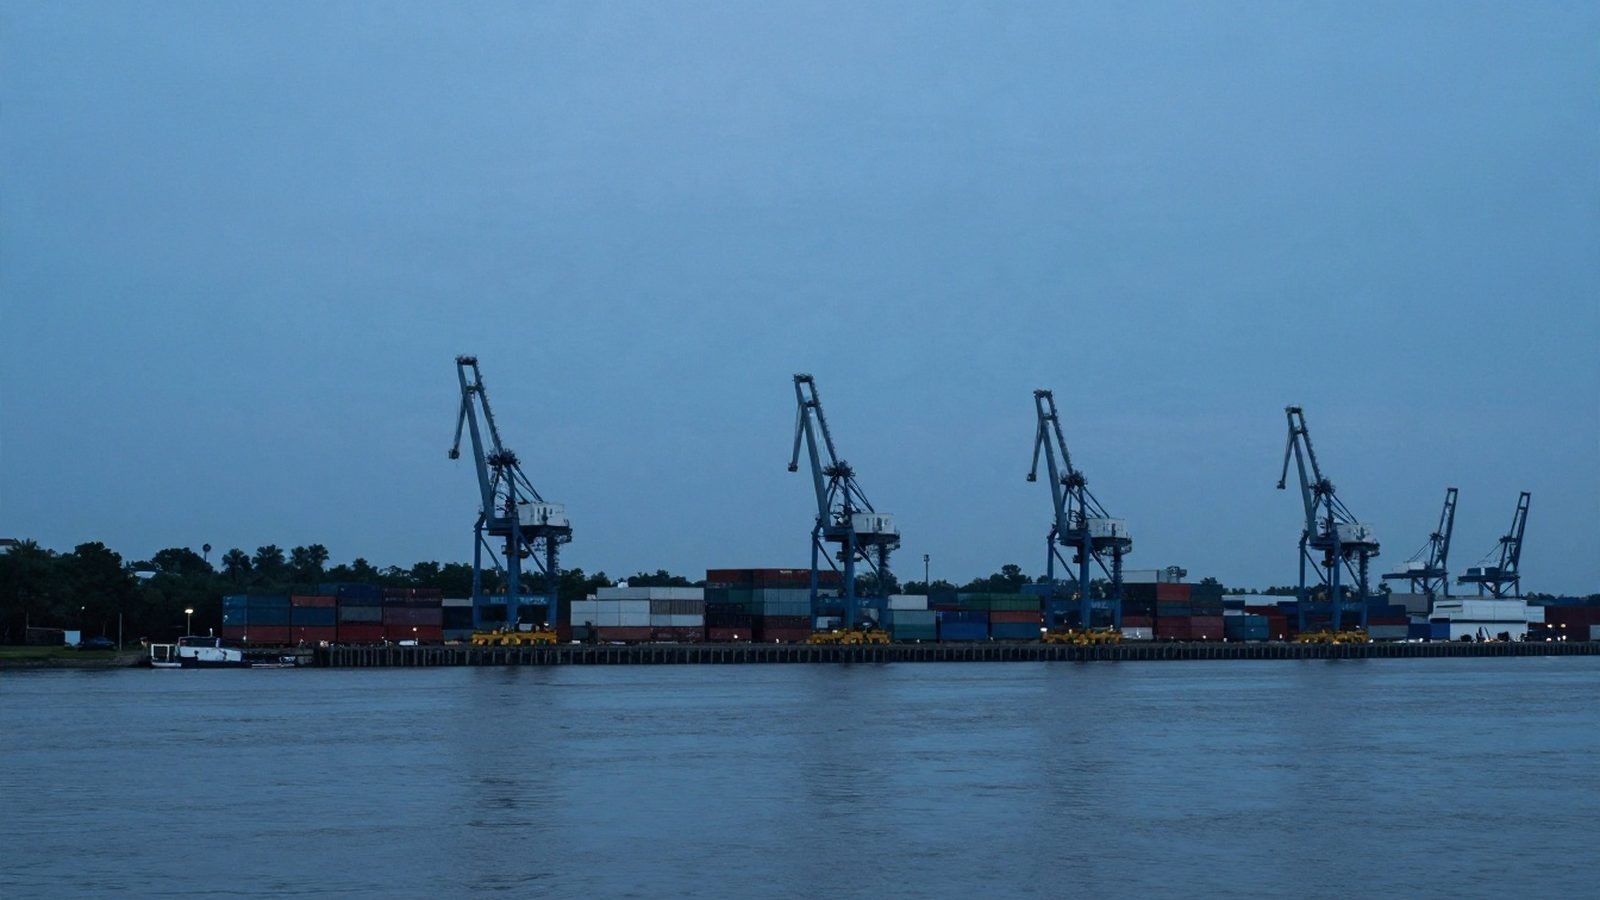
Georgia's economy is built on moving money and moving goods, and its attack surface follows both. Metro Atlanta processes a large share of US card transactions through payment processors, acquirers, point-of-sale vendors and the fintechs built on top of them, which makes it a standing target for e-skimming, API abuse, account takeover and intrusions aimed at cardholder-data environments. The same region hosts global headquarters in aviation, retail, logistics, beverages and consumer credit, whose treasury, procurement and supplier-payment functions draw business email compromise at scale. Savannah runs one of the busiest container ports in the United States, and its terminal operators, freight forwarders, warehousing and the automotive and battery plants that have grown up around it depend on operational technology and partner integrations that an attacker can use to stop cargo or production. Health systems such as Emory Healthcare, Piedmont, Northside, Wellstar and Grady face the same ransomware pressure on clinical systems that hospitals nationwide have absorbed since 2020. Augusta's Fort Eisenhower, home of US Army Cyber Command, and the aerospace sites in Marietta, Savannah and Warner Robins anchor a defence supplier base subject to CMMC. The public sector has felt the consequences directly: in January 2024 a LockBit ransomware attack took down phone, court and tax systems in Fulton County, the state's most populous county, and services were restored on a rolling basis over the following weeks. Georgia's own rules focus on notification: the Georgia Personal Identity Protection Act requires notice to affected residents in the most expedient time possible and without unreasonable delay, while state agencies follow the security standards of the Georgia Technology Authority. In Georgia scopes the recurring findings are payment APIs that trust client-side input, test and staging environments holding production card data, partner VPN tunnels with shared credentials, and flat warehouse and terminal networks reachable from office IT.
Need a penetration test in Georgia?
Written scope, named OSCP-certified testers, report within a week of the last testing day.
Georgia industries we test
Where a Georgia organisation sits in the payment, freight or care chain decides what an attacker wants from it, and therefore what we test first.
Payments, fintech & card processing (Atlanta, Alpharetta)
Payment processors, merchant acquirers, point-of-sale and payment-terminal vendors, card issuers and the fintechs of Transaction Alley. Manual web-application and API pentests, cardholder-data-environment segmentation testing, cloud and identity assessments, and red team operations against payment infrastructure. Evidence aligned to PCI DSS v4.0.1 Requirement 11.4, the GLBA Safeguards Rule and SOC 2.
Logistics, ports & transportation (Savannah, Atlanta)
Terminal operators, freight forwarders, carriers, warehousing and the aviation and parcel networks headquartered in the state. IT/OT segmentation review across terminal, warehouse and yard systems, partner-integration and EDI testing, supplier remote-access assessments, and reporting that supports the US Coast Guard's maritime cybersecurity requirements for regulated facilities.
Healthcare & public health
Academic and regional health systems in Atlanta, Augusta, Macon and Savannah, physician groups, and the health-tech and public-health data vendors around the CDC and Emory. HIPAA Security Rule technical evaluation evidence (45 CFR 164.308(a)(8)), clinical-network and medical-device segmentation testing, identity-led methodology, and breach-readiness mapped to the Georgia notification act.
Consumer credit, banking & insurance
Consumer-credit and data companies, bank holding companies, community banks, credit unions and insurers across metro Atlanta. External and internal pentests, privileged-access and identity assessments, and BEC-resilience phishing simulation. Evidence aligned to the FFIEC IT Examination Handbook, the GLBA Safeguards Rule (16 CFR Part 314), SEC Regulation S-P and the expectations of the Georgia Department of Banking and Finance.
Defence, aerospace & cyber (Augusta, Marietta, Warner Robins)
Contractors serving Fort Eisenhower and US Army Cyber Command, Robins Air Force Base and the aerospace manufacturing sites in Marietta and Savannah. CMMC 2.0 Level 2 readiness testing against NIST SP 800-171, controlled-unclassified-information boundary testing, and red team operations scoped against state-actor tradecraft, with CUI-safe handling and reporting.
Manufacturing, automotive & state and local government
Automotive and battery plants in the Savannah and West Point regions, food and consumer-goods manufacturers, and the counties, cities, school districts and agencies that hold resident data. Plant-network testing with passive-first methodology, external perimeter and web-application testing, Active Directory assessments, and evidence aligned to Georgia Technology Authority standards and NIST SP 800-53 Rev. 5.
Georgia and federal requirements our reports map to
Assessors in Georgia's payment and logistics sectors want to trace every requirement to a test. HackersHub reports are written for that trace: scope and methodology up front, CVSS-scored findings with proof, an attack narrative linking them, prioritised fixes, and a verification retest of medium and higher findings inside 90 days.
- Georgia Personal Identity Protection Act (O.C.G.A. 10-1-910 et seq.): breach notice to affected residents in the most expedient time possible and without unreasonable delay, and to consumer reporting agencies when more than 10,000 residents are notified
- Georgia Technology Authority enterprise security policies and standards for state agencies
- Georgia Department of Banking and Finance supervision of state-chartered banks, credit unions and money transmitters
- PCI DSS v4.0.1 Requirement 11.4 penetration testing and Requirement 11.4.5 segmentation testing
- Federal banking guidance (FFIEC) and the FTC's Safeguards Rule under GLBA
- 45 CFR 164.308(a)(8): the HIPAA evaluation standard for hospitals and health-tech vendors
- US Coast Guard cybersecurity rule for the marine transportation system (33 CFR Part 101, effective 2025) for regulated port facilities and vessels
- TSA security directives for aviation and surface transportation operators
- Defense Department CMMC program, Level 2 (NIST SP 800-171 controls)
- AICPA SOC 2 Trust Services Criteria, notably CC7.1 and CC7.4
- NIST SP 800-115 for test planning and execution
Services available in Georgia
Start with the asset that worries your assessor most, whether that is a payment API, a terminal network or a CUI enclave, and extend from there.
See also:Penetration Testing in AtlantaPenetration Testing in FloridaPenetration Testing in United States
Why payment and logistics teams in Georgia work with HackersHub
Payments and technology are among the sectors HackersHub has served longest, and fintech is part of the initial focus for the firm's full-scale US market entry in Q1 2027. That entry is still ahead: today HackersHub is headquartered in Amsterdam, has no US office, and serves US clients from the Netherlands together with US delivery partners. For a Georgia processor or SaaS platform the model is practical, because API, web-application, cloud and external testing runs over the network and calls are scheduled on Eastern Time. When a scope includes a warehouse floor in Savannah, a cardholder-data segment in an Alpharetta data centre or a physical-access test, testers travel to the site. Experience is measured in more than 2,500 engagements since the firm was founded in the Netherlands in 2015. Certification is not optional: every tester holds OSCP, specialists hold OSWE or CREST, and Michael van Mameren (OSCP) leads delivery. Reports follow PTES, the OWASP WSTG and NIST SP 800-115, and pricing is a custom quote per scope rather than a published rate card.
Frequently asked questions: Georgia
Ready to Secure Your Systems?
Request a quote for your penetration testing needs.